

Key takeaways
• ONVIF is the only viable multi-vendor standard in physical security. Axis, Bosch and Sony founded it in 2008. Today it covers seven active profiles, more than 30,000 conformant products (ONVIF, August 2024) and about 500 member companies (ONVIF, September 2026), and almost every enterprise IP camera and VMS worth shortlisting speaks it.
• ONVIF profiles are a la carte, not a cumulative stack. A camera implements S or T for streaming, G for edge recording and M for analytics metadata, plus A, C and D when access control is in scope. One profile never implies another.
• Profile T is the 2026 baseline, and Profile S is being retired. ONVIF stops accepting new Profile S conformance on March 31, 2027, because Profile S mandates username-token auth that falls short of current security guidance. Spec Profile T on every new deployment.
• Profile V (release candidate since July 2026, final expected by end of 2026) finally standardizes cloud video. It defines device-initiated Uplink, OAuth 2.0 auth and WebRTC streaming to a cloud VMS, so a VSaaS product no longer has to tie you to one vendor's proprietary cloud.
• Only the Conformant Products List is authoritative, and ONVIF is the floor, not the ceiling. Check each camera's Declaration of Conformance instead of the spec sheet. Vendor AI (Axis ACAP, Bosch IVA, Hanwha Wisenet AI) never flows through ONVIF, so if a feature depends on it, budget for a hybrid SDK path.
Updated November 2026: the FCC’s component rule in force since October 13, 2026 (FCC 26-50), ONVIF specification release 26.06 and Profile V Release Candidate 2.0, and a corrected Profile G scope.
Why Fora Soft wrote this playbook
Fora Soft is a software development company that has built video and real-time communication software since 2005. In 20+ years and 250+ delivered products we have shipped more ONVIF-backed VMS, NVR, body-worn, courtroom and analytics projects than we can comfortably list. ONVIF matters more than any other interoperability standard in IP surveillance, and people misread it more than any other. Nine out of ten integrators who call us already own the hardware and the VMS and can't work out why the two won't talk. Almost every time, the cause is a profile mismatch nobody checked.
This guide is the briefing we give a client in week one of a new surveillance project. It covers what each ONVIF profile does, where it breaks, which profile to mandate, how to check conformance in minutes, and where you will end up on vendor SDKs anyway. We checked it against real deployments, including VALT, the enterprise video surveillance platform we have been the sole development team behind for over a decade, now used by 770+ US organizations and 50,000+ users under HIPAA. Our video surveillance development services page shows the kind of work this playbook comes out of.
Weighing up ONVIF versus a vendor SDK?
Thirty minutes with a Fora Soft engineer saves weeks of integration pain on camera shortlisting and VMS architecture.
What ONVIF actually is (and isn’t)
ONVIF (Open Network Video Interface Forum) is a non-profit industry consortium founded in 2008 by Axis Communications, Bosch Security Systems and Sony. Its charter is narrow: open standards for the interfaces between IP-based physical security products. It publishes the specifications, runs conformance testing and keeps a public list of conformant products, which passed 30,000 devices and clients in August 2024. ONVIF counts about 500 member companies as of September 2026. It covers only the interfaces between devices; recording, search, analytics and alerting live in the video management software that consumes them.
On the wire, ONVIF defines web services as SOAP 1.2 over HTTP(S) with WSDL contracts, plus RTSP/RTP for media. Authentication uses Digest or WS-Security UsernameToken. Events go out as SOAP notifications, pull-point or base, and since Profile M they can also go over MQTT with JSON payloads. Devices find each other on the LAN with WS-Discovery.
ONVIF versions its network interface specifications twice a year, in June and December. Release 26.06 (June 2026) is the latest, and it added SRTP support to the streaming specifications. Profiles and add-ons have their own version numbers on top, so “ONVIF version” on a datasheet tells you little until you know which profile and which release it means.
What ONVIF is not. It is not a video format: H.264 and H.265 are codecs. It is not a cloud platform or a management UI, and it ships no reference hardware. It also never standardizes proprietary features. Axis ACAP, Bosch IVA, Hikvision AcuSense and Hanwha Wisenet AI all sit outside the spec, even on ONVIF-certified cameras.
Why ONVIF won the standards war
The only real rival, PSIA (Physical Security Interoperability Alliance, also founded 2008), had a wider scope and used REST instead of SOAP. It looked cleaner on paper and had few allies in practice. ONVIF had the three founding manufacturers, then Hanwha, Pelco, Hikvision and Dahua, and the market followed them. PSIA still exists, but nobody picks it for new deployments, and an integrator who says otherwise is a decade out of date.
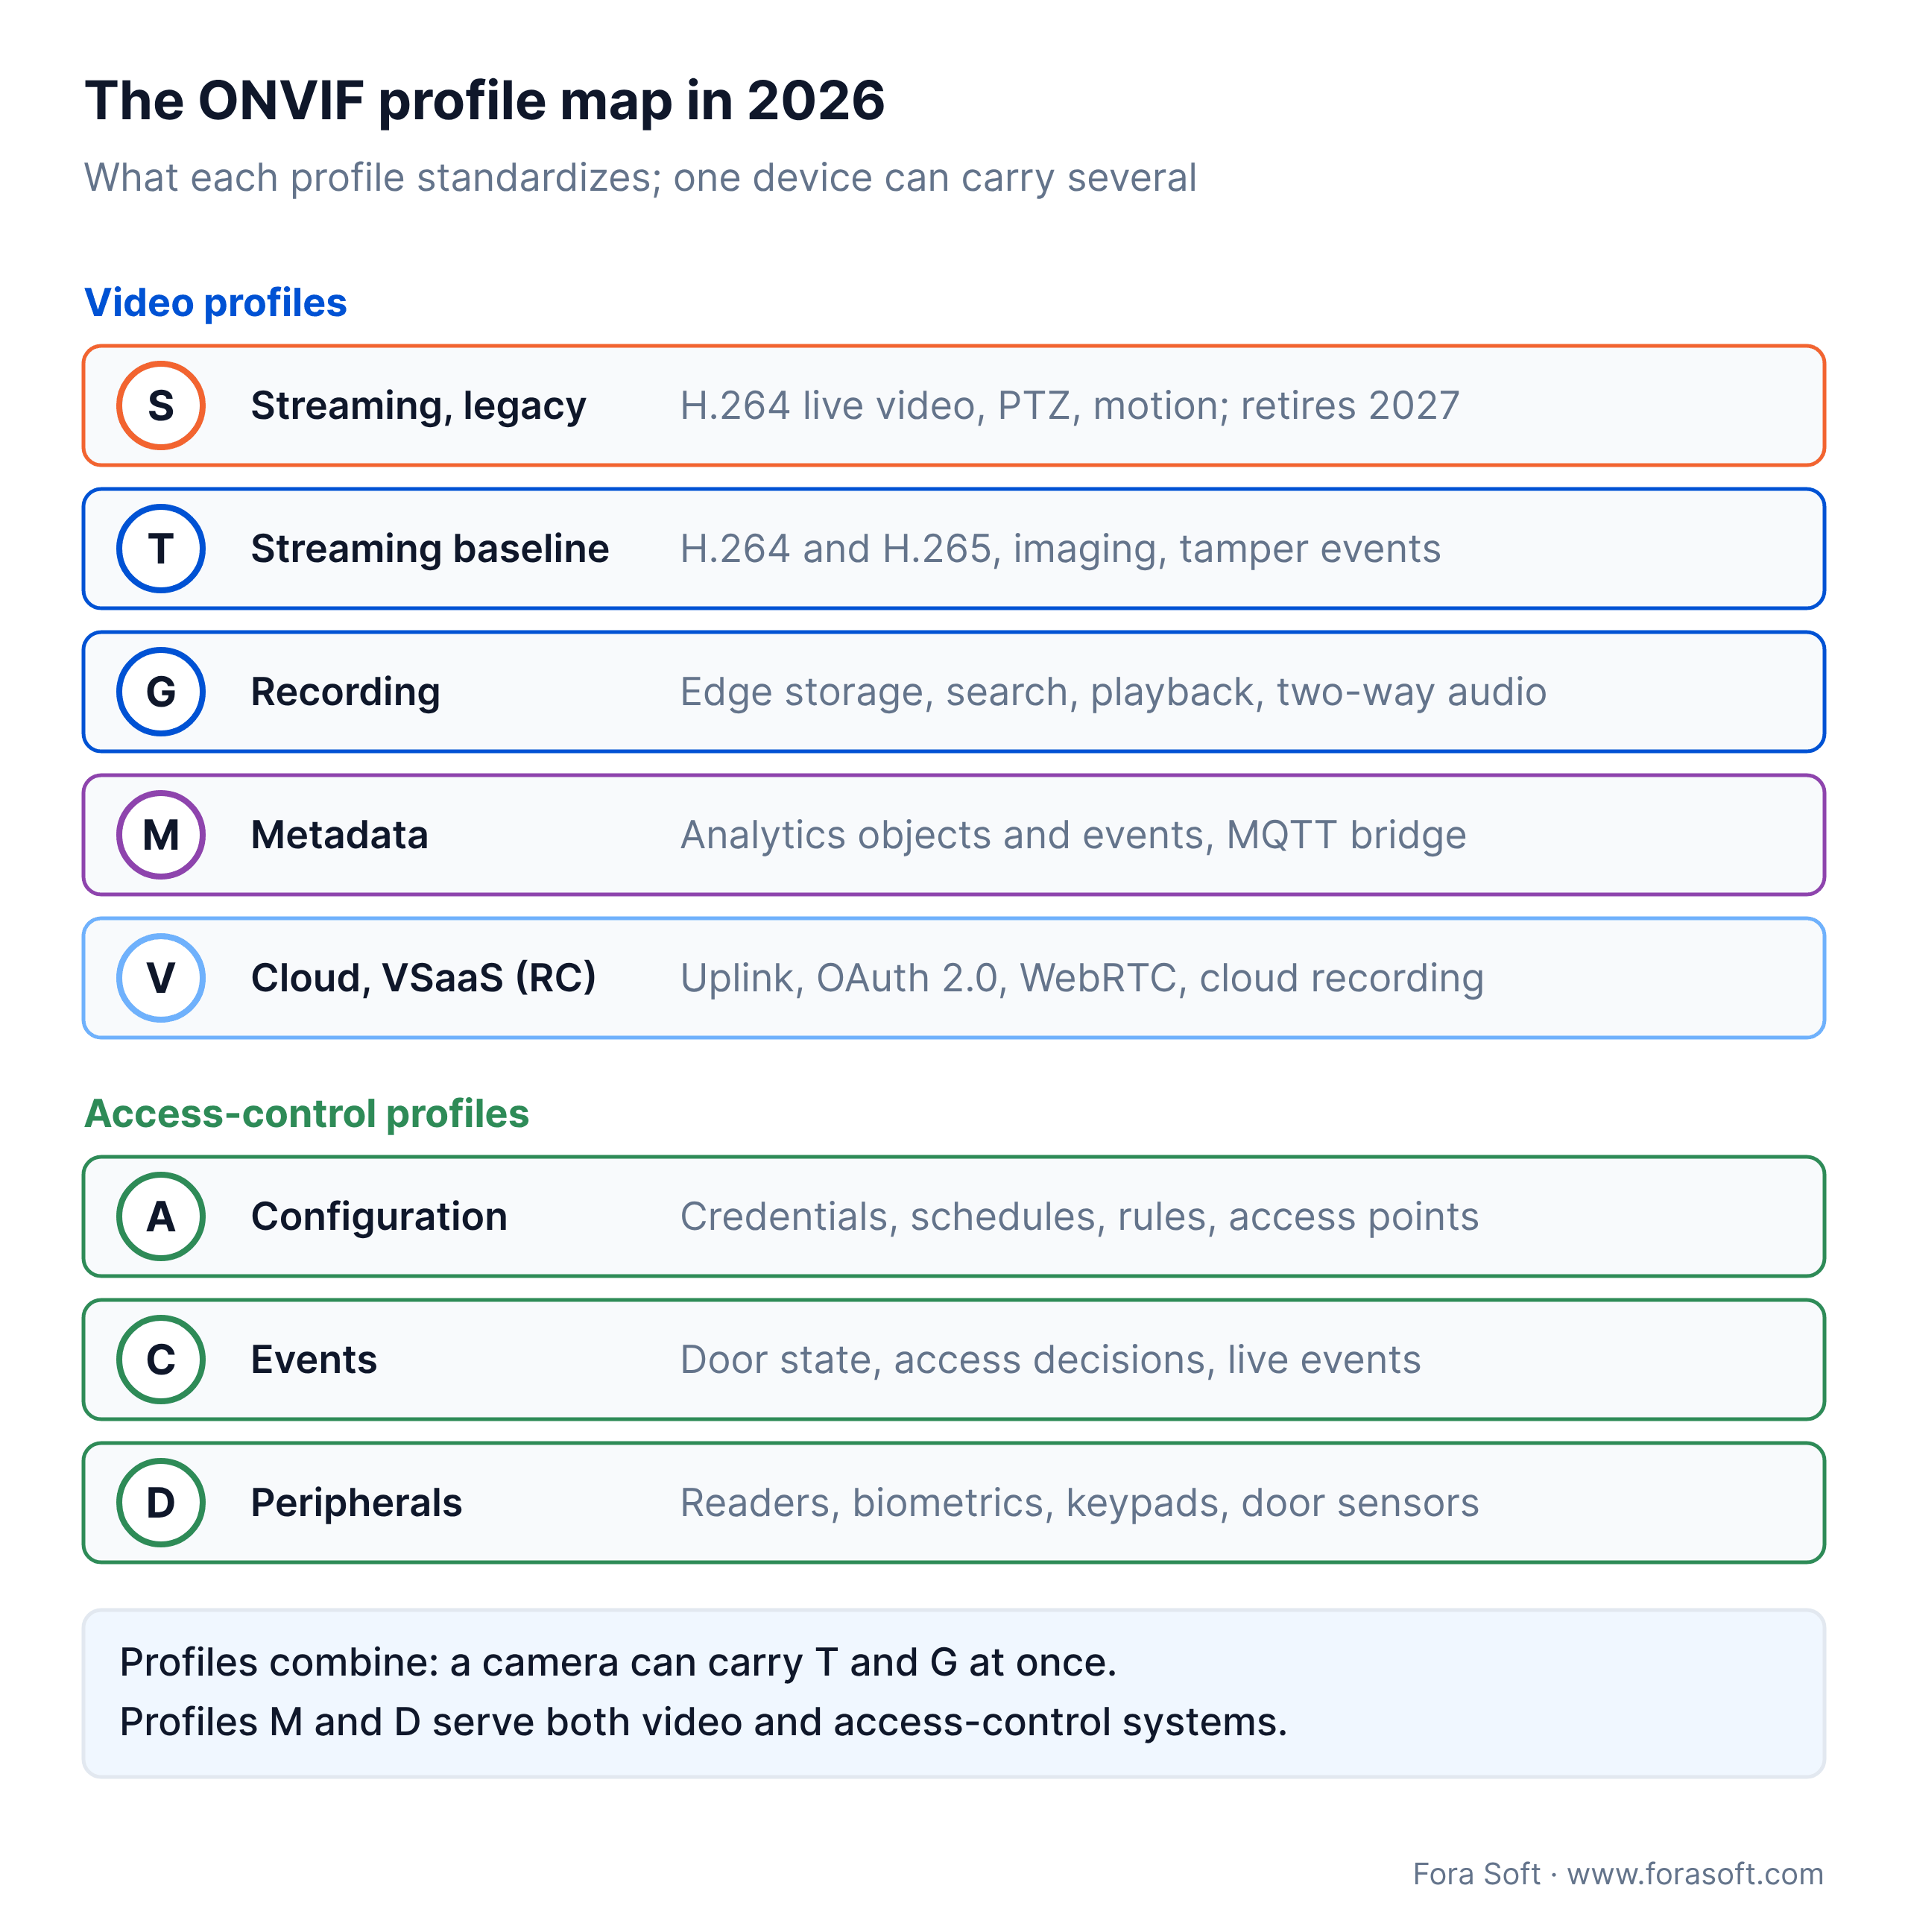
Figure 1. The 2026 ONVIF profile map: what each video and access-control profile standardizes, and which combine on a single device.
The ONVIF profile roster at a glance
In 2026 there are seven active profiles, plus Profile V, a cloud profile in release-candidate status, and a small set of modular add-ons. Profile Q was deprecated on April 1, 2022 for security reasons. The table below is the full map.
| Profile | Domain | Baseline use case | Status in 2026 |
|---|---|---|---|
| S | Video streaming | H.264 live video, basic PTZ, motion events. | Retiring: no new conformance after Mar 31, 2027. |
| T | Advanced streaming | H.265, embedded analytics, tamper events, image settings. | Current baseline for new projects. |
| G | Recording + playback | Edge storage, search, retrieval, playback. | Still the only option for edge recording. |
| M | Metadata + analytics | Object detection, classification, events, MQTT bridge. | Growing fast on enterprise AI cameras. |
| A | Access control config | Credentials, schedules, rules, access-point config. | Mature; pairs with C on every ACS. |
| C | Access control events | Door state, access decisions, real-time events. | Always paired with A in practice. |
| D | Access peripherals | Readers, biometrics, keypads, door sensors. | Finalized 2021; adoption uneven. |
| V | Cloud / VSaaS | Uplink, OAuth 2.0, WebRTC streaming, cloud recording. | Release candidate; finalizing end of 2026. |
| Q | (deprecated) | Out-of-box configuration; retired Apr 1, 2022. | Do not rely on; security concerns. |
Reach for the T + G + M bundle when: you are building a modern IP-camera VMS. Add A + C for access control, add D only if peripherals are in scope, and watch Profile V if the product is cloud-first.
Profile S: the streaming baseline retiring in 2027
ONVIF Profile S is the basic IP video streaming profile: live H.264 video, audio, PTZ and motion events between a camera and a VMS. Finalized in 2011, it was the first ONVIF profile and for a decade the default sticker on every IP camera box. It standardizes live H.264 video, audio streaming, PTZ control, motion-detection events and basic metadata. A VMS that supports exactly one ONVIF profile almost always supports Profile S.
The 2027 deadline changes procurement now. On October 9, 2025 ONVIF announced it is ending support for Profile S and recommending Profile T as the successor. After March 31, 2027, manufacturers can no longer submit new products, or existing products with new firmware, for Profile S conformance. The reason is security: Profile S mandates username-token authentication, which current cybersecurity recommendations no longer accept. Existing Profile S devices keep working, but if you specify hardware in 2026, treat Profile S as a legacy fallback and mandate Profile T.
What it misses. H.265, image-setting management, embedded analytics and proper tamper events are all absent. On a new 2026 deployment a Profile S-only stack gives up roughly 50% of bandwidth savings and every analytics capability.
Profile T: the 2026 streaming baseline
Profile T was finalized on October 25, 2018, and it is the streaming profile to default to today. It adds H.265 alongside H.264, embedded motion and tampering analytics, image-settings management (brightness, contrast, WDR), bidirectional audio and better event handling. One detail trips teams up: a Profile T client must handle both H.264 and H.265, while a Profile T device needs only one of them. Confirm H.265 on the specific model instead of assuming the profile guarantees it.
Why it matters commercially. H.265 cuts storage and bandwidth by roughly 50% versus H.264 at the same visual quality. On a 1,000-camera site that turns a $12k/month storage bill into a $6k/month one. A VMS that is still Profile S-only pays that difference for nothing. Our notes on the pipeline side are in real-time video processing with AI.
ONVIF Profile S vs T: which one to specify
Specify Profile T. It covers nearly every Profile S feature and adds H.265, image settings, tamper and motion analytics events and stronger authentication. According to ONVIF’s Profile S deprecation Q&A, only three Profile S features did not carry over to Profile T: username-token authentication, IP address filtering and MJPEG/MPEG-4 video. Products may still support them natively, outside conformance.
| Capability | Profile S | Profile T |
|---|---|---|
| Video codecs | H.264 (MJPEG/MPEG-4 on older devices) | H.264 and H.265 (client must handle both, device at least one) |
| Authentication | Username token required | Digest; TLS/HTTPS recommended |
| PTZ and audio | PTZ, audio out | PTZ, bidirectional audio |
| Image settings (WDR, brightness) | Not standardized | Standardized |
| Analytics events | Motion only | Motion and tampering |
| Conformance status | No new submissions after March 31, 2027 | Current streaming baseline |
Existing Profile S products stay conformant until the manufacturer withdraws its Declaration of Conformance, so you don't have to rip them out. The real risk is firmware. If a vendor disables username-token authentication in a new release, that device becomes non-conformant and a VMS integration that still logs in that way can break. Pin firmware and move clients to digest or TLS now.
Profile G: edge recording and playback
ONVIF Profile G is the edge recording and playback profile. Finalized in 2014, it covers NVRs, edge-recording cameras with SD cards or internal storage, and any device that records video locally. It standardizes four things: recording schedules, recording metadata queries, recording retrieval and playback control. The mandatory core is small: HTTP digest authentication, recording search and replay control. A Profile G device can also send audio and metadata with the recorded video when the client supports them; two-way audio belongs to Profile T. The current Profile G specification, version 1.1 dates from October 2025 and only made an editorial correction, so a Profile G DoC from earlier years still describes the same feature set.
Profile G is essential wherever centralized storage won't work: remote sites, vehicles, temporary installations, body-worn cameras. It is the only vendor-neutral way for a VMS to query an edge-stored archive without a proprietary SDK. We cover the architecture trade-offs in scalable video management systems.
Profile M: the analytics metadata profile
Profile M, published in 2021, is the newest streaming-adjacent profile. It standardizes how IP devices share analytics metadata: bounding boxes, classifications (human, vehicle, face, license plate), events (line crossing, counting, loitering) and geolocation. It also adds an optional MQTT binding for events, so your data platform can subscribe to a camera like any other IoT node.
Profile M is spreading quickly on enterprise AI cameras (Axis ARTPEC-9, Bosch 7000 series, Dallmeier, Hanwha Wisenet P/X, Pelco Sarix). Mid-tier and budget brands still keep their best analytics behind proprietary SDKs. The metadata side gets its own ONVIF Profile M and object detection guide.
Profile V: the cloud profile arriving in 2026
ONVIF Profile V is the cloud video surveillance (VSaaS) profile: it lets cameras from different vendors connect out to one cloud VMS. ONVIF published the Profile V release candidate on July 9, 2026, opened it for member review and expects to finalize it by the end of 2026. As of November 2026 the ONVIF profiles page lists it as Release Candidate 2.0, together with Release Candidate 2.0 of the Profile V Security Add-on. It is the first credible standard for building a cloud VMS from cameras of more than one vendor, with no brand's proprietary cloud in the middle. If you have watched a customer get locked into a single VSaaS vendor, that is the part that matters.
How it works. The camera sits behind a local firewall and opens an outbound Uplink connection to the cloud client over WSS (WebSocket Secure), so you need no port forwarding and no VPN. Authentication uses the OAuth 2.0 framework with mutual TLS and access tokens. The device then streams low-latency H.264 video over WebRTC, pushes encrypted video and audio to cloud storage such as Amazon S3 or Azure Blob for recording, and sends events as pull-point notifications over the Uplink or as JSON over MQTTS. Bidirectional audio goes over WebRTC where the hardware supports it.
Why the security lives in an add-on. Profile V comes paired with a Profile V Security Add-on that holds the OAuth 2.0 requirements and the recording encryption. ONVIF split those rules out so it can upgrade them as threats change without rewriting the whole profile. If you are scoping a cloud camera product for 2026 or 2027, design toward Profile V now. It maps almost exactly onto the VSaaS architecture teams already build by hand.
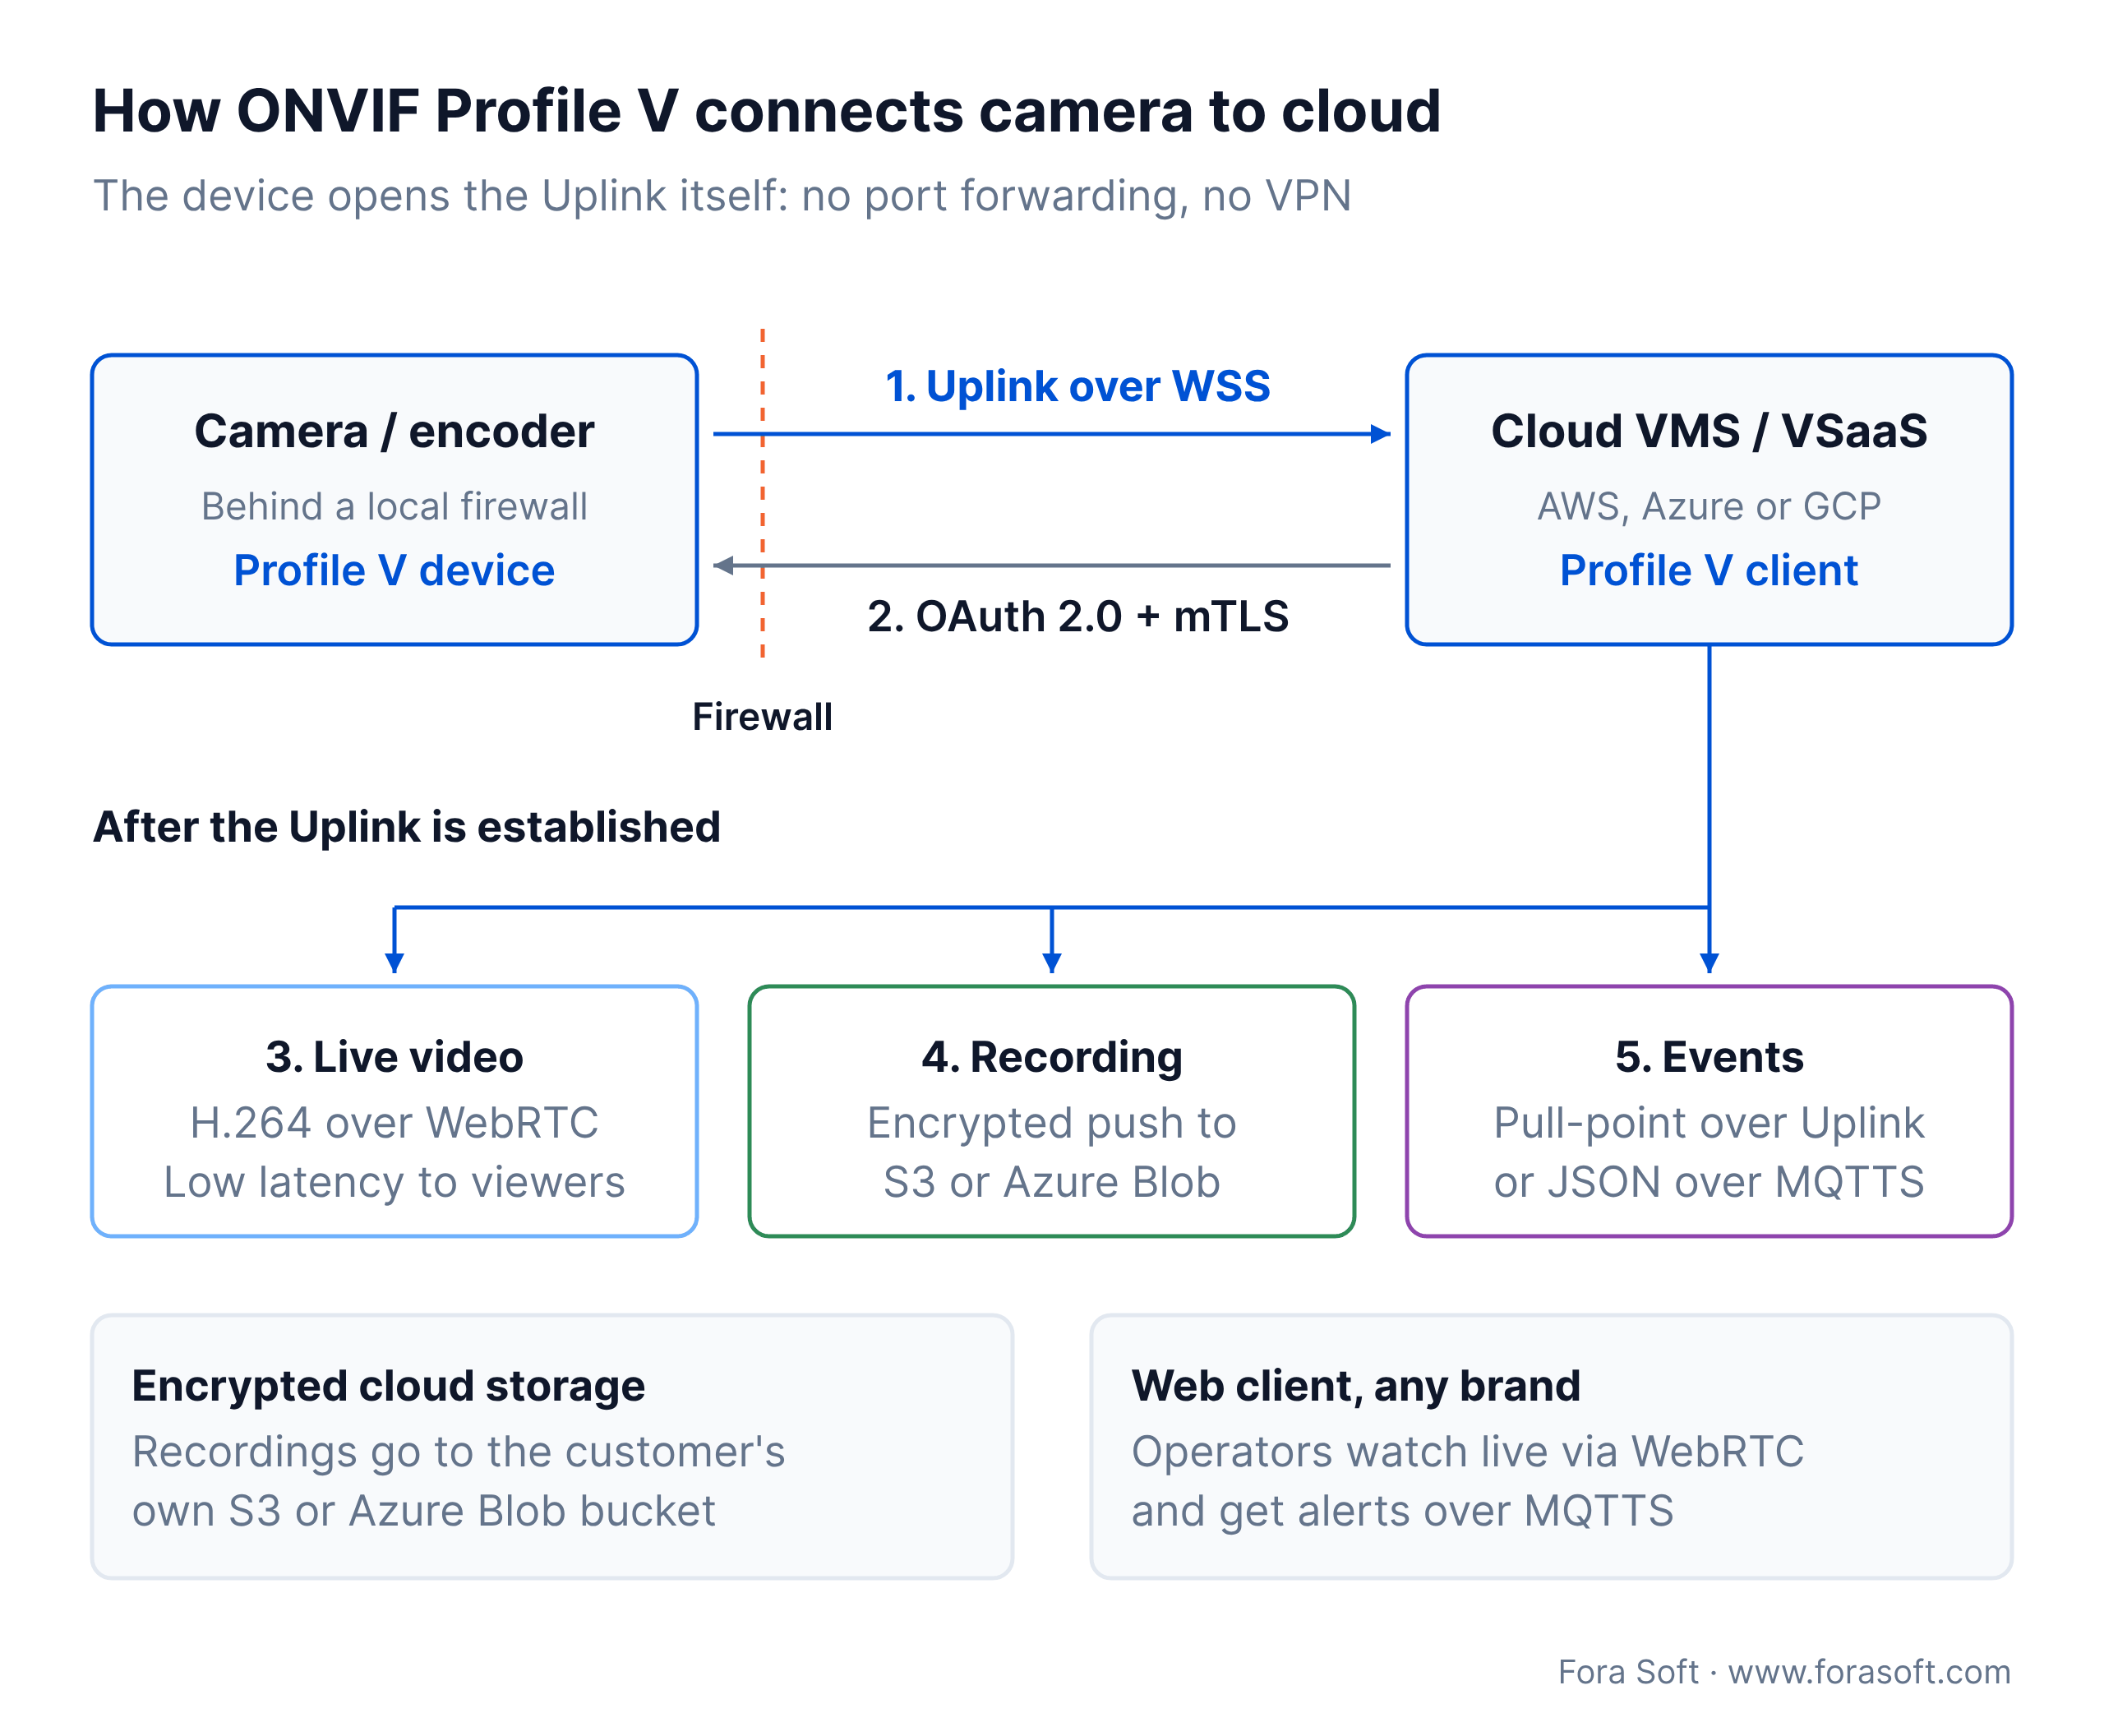
Figure 2. Profile V connection flow: the device initiates a secure Uplink to the cloud client, then streams over WebRTC and records to cloud storage.
Reach for Profile V when: you are building a cloud-first VMS or VSaaS and want cameras from multiple brands to work against one cloud backend. It is still a release candidate, so pin conformance dates and keep a fallback path until devices ship with it. The cloud side is ordinary WebRTC engineering (signaling, TURN, SFU fan-out to many viewers), and our WebRTC software development team builds that receiving end for VSaaS products today.
Profiles A, C, D: the access-control triad
For years video overshadowed ONVIF's access-control profiles. Now that surveillance and physical access control systems (PACS) are converging, these three profiles deserve a closer look.
Profile C (finalized 2013) handles run-time events: door-state notifications, access-granted or denied events, operational status. A VMS subscribes to Profile C to show door events next to a live camera feed.
Profile A (finalized 2017) handles configuration: credentials, schedules, access rules and access-point definitions. It is the management surface of an access control system.
Profile D (finalized 2021) handles peripherals: RFID and QR readers, biometric devices, keypads, door sensors and request-to-exit buttons. It is the youngest of the three, adoption is uneven, and many deployments still run on proprietary reader SDKs.
Reach for Profiles A + C + D as a bundle when: you are building a unified video and access control product. Skip D if you plan to keep vendor-specific reader SDKs for now; A + C alone still give you a clean, unified event flow.
ONVIF add-ons: TLS 2.0, Media Signing, Profile V Security
Add-ons are small, versioned specifications that extend an existing profile and cannot stand alone. A product must already conform to at least one profile before it can claim an add-on. Since add-ons have their own version numbers, security requirements can move faster than the profiles they attach to. As of November 2026 ONVIF lists three add-on tracks: TLS Configuration (with version 2.0 in release candidate), Profile V Security and Media Signing. The last two are also release candidates, with final specifications expected at the end of 2026.
TLS Configuration Add-on. ONVIF's first add-on came out as a release candidate in 2023, and the v1.0 specification followed in early 2024. It lets a conformant VMS configure or update TLS settings on a conformant device, so you provision encrypted client-device communication centrally instead of setting it up camera by camera. On September 9, 2026 ONVIF published the TLS Configuration Add-on 2.0 release candidate with stronger methods for protecting device-to-VMS traffic; the final 2.0 specification is expected at the end of 2026.
Media Signing Add-on. Announced on August 26, 2026 as a release candidate, it has the camera or encoder sign video cryptographically at the moment of encoding. A player can later prove the footage is authentic and trace it to the device, even after export and sharing. Version 1 covers video only, with audio planned later, and ONVIF published the signing and verification framework code on its GitHub. For evidence-grade systems (courtrooms, police interview rooms, insurance) this is the first vendor-neutral answer to “prove this clip was not edited”.
Profile V Security Add-on. Released together with the Profile V candidate, it defines OAuth 2.0 authentication between a device and a cloud-based client and encrypts recordings on their way to storage. Without it, the Profile V cloud model would not be safe to deploy across vendors.
Uplink. The ONVIF Uplink specification is not an add-on. It is the base of the cloud story: it defines the device-initiated outbound channel, secured with TLS, that Profile V uses to reach a client through a firewall. When you read a Profile V or add-on Declaration of Conformance, check the version number, because a 1.2 add-on is not automatically compatible with a 1.0 client.
Need an ONVIF-native VMS without the yak-shaving?
We have built ONVIF consumers for retail, smart-city, industrial and courtroom deployments. Bring your shortlist, we will bring the estimate.

Figure 3. ONVIF profile timeline, from Profile S in 2011 to Profile V in 2026 and the Profile S sunset on March 31, 2027.
Verifying conformance in five minutes
The only authoritative source is the ONVIF Conformant Products List. ONVIF itself warns that spec sheets often misuse the logo and overstate conformance, so treat every marketing page as suspect. The Declaration of Conformance (DoC) is the contract.
The 6-step DoC workflow
1. Find the exact model. Search the Conformant Products database by manufacturer and model number. Watch for model revisions: a DS-2CD2663G0 is not a DS-2CD2663G1.
2. Match the firmware. Each DoC is tied to a tested firmware version. If your stock runs other firmware, that DoC does not apply.
3. Download the DoC. The first page lists the profiles claimed, for example “Profile S, T, G, M”.
4. Scan the feature tables. Every feature is marked M (mandatory, must work), C (conditional, must work if the functionality exists at all), or O (optional). Check that the features you need are ticked; don't assume them.
5. Cross-check with a live tool. ONVIF Device Manager (free, Windows-only) connects to the camera and lists the services it supports. Compare that list with the DoC.
6. Pin the firmware. Lock the exact firmware version in your deployment bill of materials and add a re-test step for every firmware upgrade.
The toolchain that keeps an ONVIF project moving
ONVIF Device Manager (Windows, free). Still the fastest way to connect to a camera, list its services, check DoC claims and pull a test stream.
ONVIF Device Test Tool (members only). The official conformance suite that manufacturers run. If you build devices instead of consuming them, you will spend most of your test time in it.
gSOAP, python-zeep and onvif-zeep. WSDL-to-code generators for C/C++ and Python clients. Keep local copies of the ONVIF WSDLs, because resolving them online breaks easily.
Wireshark with RTSP and SOAP dissectors. When the DoC says one thing and the camera does another, the packet capture settles it.
Happytime ONVIF Server and other emulators. Spin up a synthetic device and test your VMS consumer without touching physical hardware. More builder notes are in our video surveillance engineering hub.
Building an ONVIF device: reference designs and open source
ONVIF ships no reference hardware or reference firmware. It does publish the specification source: since September 2020 the schema and specification files have lived in the public onvif/specs GitHub repository, and members get the Device Test Tool. A device “reference design” therefore comes from third parties. SoC vendors bundle ONVIF servers in their camera SDKs, and commercial kits such as the RidgeRun ONVIF Device Reference Design turn an NVIDIA Jetson board into an ONVIF camera. Check which profile a reference design targets. RidgeRun’s documents Profile S only, which is fine as a starting point but will not carry a product past 2027, so plan Profile T on top.
For live interoperability testing, ONVIF holds Developers’ Plugfests twice a year in different regions; check the ONVIF events page for the next date before you plan a certification sprint around one.
The profile bundles you actually deploy
| Deployment | Required profiles | Typical gear |
|---|---|---|
| Entry-level small office | T (S only on legacy stock) | 4–16 IP cameras + basic NVR. |
| Modern small-to-mid | T + G | 4K H.265 cameras, edge SD recording, central VMS. |
| Enterprise AI surveillance | T + G + M | Analytics cameras, metadata store, MQTT broker. |
| Campus with access control | T + G + M + A + C | Above + door controllers, card readers, unified UI. |
| Cloud-first / VSaaS | V (+ T on-prem fallback) | Uplink cameras, cloud VMS, S3/Azure recording. |
| Distributed low-connectivity | T + G (heavy edge) | Body-worn, vehicle, remote sites with intermittent backhaul. |
Vendor adoption and the NDAA/FCC reality
Enterprise. Axis, Bosch, Hanwha, Pelco and Dallmeier publish clean DoCs, maintain firmware and keep Profile M current. With these brands, “ONVIF compliant” on the box matches the DoC in the database.
Mid-tier. Vivotek, i-PRO and Lorex offer solid Profile S and T and partial G, and are slowly adding M. Their DoCs are usually accurate, though budget SKUs drop optional features.
High-volume and budget. Hikvision and Dahua are ONVIF members and ship Profile S and T widely, but their advanced analytics and storage features sit behind proprietary ISAPI and DH-SDK interfaces. With these brands you will almost always run a proprietary SDK path next to ONVIF, so budget for it.
Cloud and VSaaS. Verkada, Eagle Eye and Spot AI put ONVIF behind a gateway: the edge camera speaks ONVIF upstream and the cloud UI is proprietary. That works, as long as you remember that ONVIF feature parity ends at the gateway. Profile V targets exactly this gap.
The compliance layer buyers cannot skip in 2026
ONVIF conformance says nothing about whether you are allowed to buy a camera. In the US that is a separate question, and the answer keeps getting stricter. NDAA Section 889 (2019) banned Hikvision, Dahua, Huawei, ZTE and Hytera from federal procurement. The FCC then added them to its Covered List, and in October 2025 moved to close the loopholes that let previously authorized gear keep entering the country. In an order issued on June 26, 2026, published in the Federal Register on July 6 and effective July 16, 2026, the FCC prohibited continued import and marketing of previously authorized covered equipment added to the Covered List in 2024 or earlier. It gave no transition period and rejected a proposed exemption for spare parts, updates and replacements; legally bought equipment already in service may keep operating.
A second rule followed. The FCC’s Third Report and Order (FCC 26-50), adopted July 22, 2026 and in force since October 13, 2026, bars new equipment authorizations for devices that contain a logic-bearing hardware component made by a Covered List company, when the device would be barred had that company built it whole. Passive parts such as housings and wiring are excluded, and the rule covers new applications only. Online marketplaces must show a valid FCC ID at the point of sale from March 1 or June 1, 2027, depending on their role. If you build an ONVIF camera, this reaches into the bill of materials: a design built on a covered vendor’s chip cannot get a new FCC authorization, whatever profiles it passes.
Nobody has to rip out existing installations, but new products, replacement parts and expansions of covered brands now face limits. The practical rule for 2026 procurement: run NDAA and FCC status as a hard filter before the ONVIF profile audit. Our guide to IP camera systems for business and AI-powered IP camera trends go deeper on sourcing.
Mini case: a 400-camera hospital migration
Situation. A regional hospital group ran a decade-old VMS with roughly 400 Axis P-series cameras on Profile S H.264. Recording was eating a central SAN, the CISO wanted HIPAA-grade audit and after-hours loitering analytics, and access-control events had to reach the SOC dashboard without one more vendor integration. We handle exactly this kind of migration on VALT, the enterprise surveillance platform we have maintained as sole development team for 10+ years across 770+ US organizations and 50,000+ users.
The 10-week plan. Weeks 1–2: DoC audit, firmware plan, and a rolling H.264-to-H.265 transition via Profile T. Weeks 3–5: Profile M on the newer P-series units, with an MQTT broker for metadata. Weeks 6–7: access-control Profile A and C integration with the existing HID readers. Weeks 8–9: audit trail and SOC UI. Week 10: load test, runbooks and handoff.
The storage math, worked. One 4 MP camera recording continuously at 4 Mbps on H.264 writes 4 × 86,400 / 8 ≈ 43 GB/day. At equal quality, Profile T H.265 lands near 2 Mbps, about 21 GB/day. Across 400 cameras that saves roughly 8.6 TB/day, or about 3.1 PB/year off the SAN. Moving to Profile M also put alerting on the metadata path: operators now watch object events (person after hours, vehicle in a fire lane) instead of raw motion, and access events appear beside the matching camera feed with no extra plugin. The VMS side is covered in 12 essential features of modern VMS software.
What an ONVIF consumer really costs to build
The estimates below assume our Agent Engineering-accelerated workflow; teams without it should budget 40–60% more hours. The numbers cover the ONVIF integration only, without the VMS UI, user management or storage plumbing around it. Analytics on top of Profile M metadata is scoped separately by our computer vision for video surveillance team.
| Scope | Fora Soft hours | Includes |
|---|---|---|
| Profile T consumer | 80–130 | Discovery, auth, RTSP, H.265, PTZ, image settings, tamper events. |
| Profile G edge storage | 60–100 | Recording schedule, search, retrieval, playback. |
| Profile M metadata | 120–180 | Scene description parsing, MQTT bridge, metadata store. |
| Profile A + C access control | 80–140 | Credentials, rules, real-time door events, UI bindings. |
| Profile V cloud path | 140–220 | Uplink/WSS, OAuth 2.0/mTLS, WebRTC, cloud recording. |
| Full modern VMS (T+G+M) | ~260–410 | Excludes UI, user management, storage plumbing. |
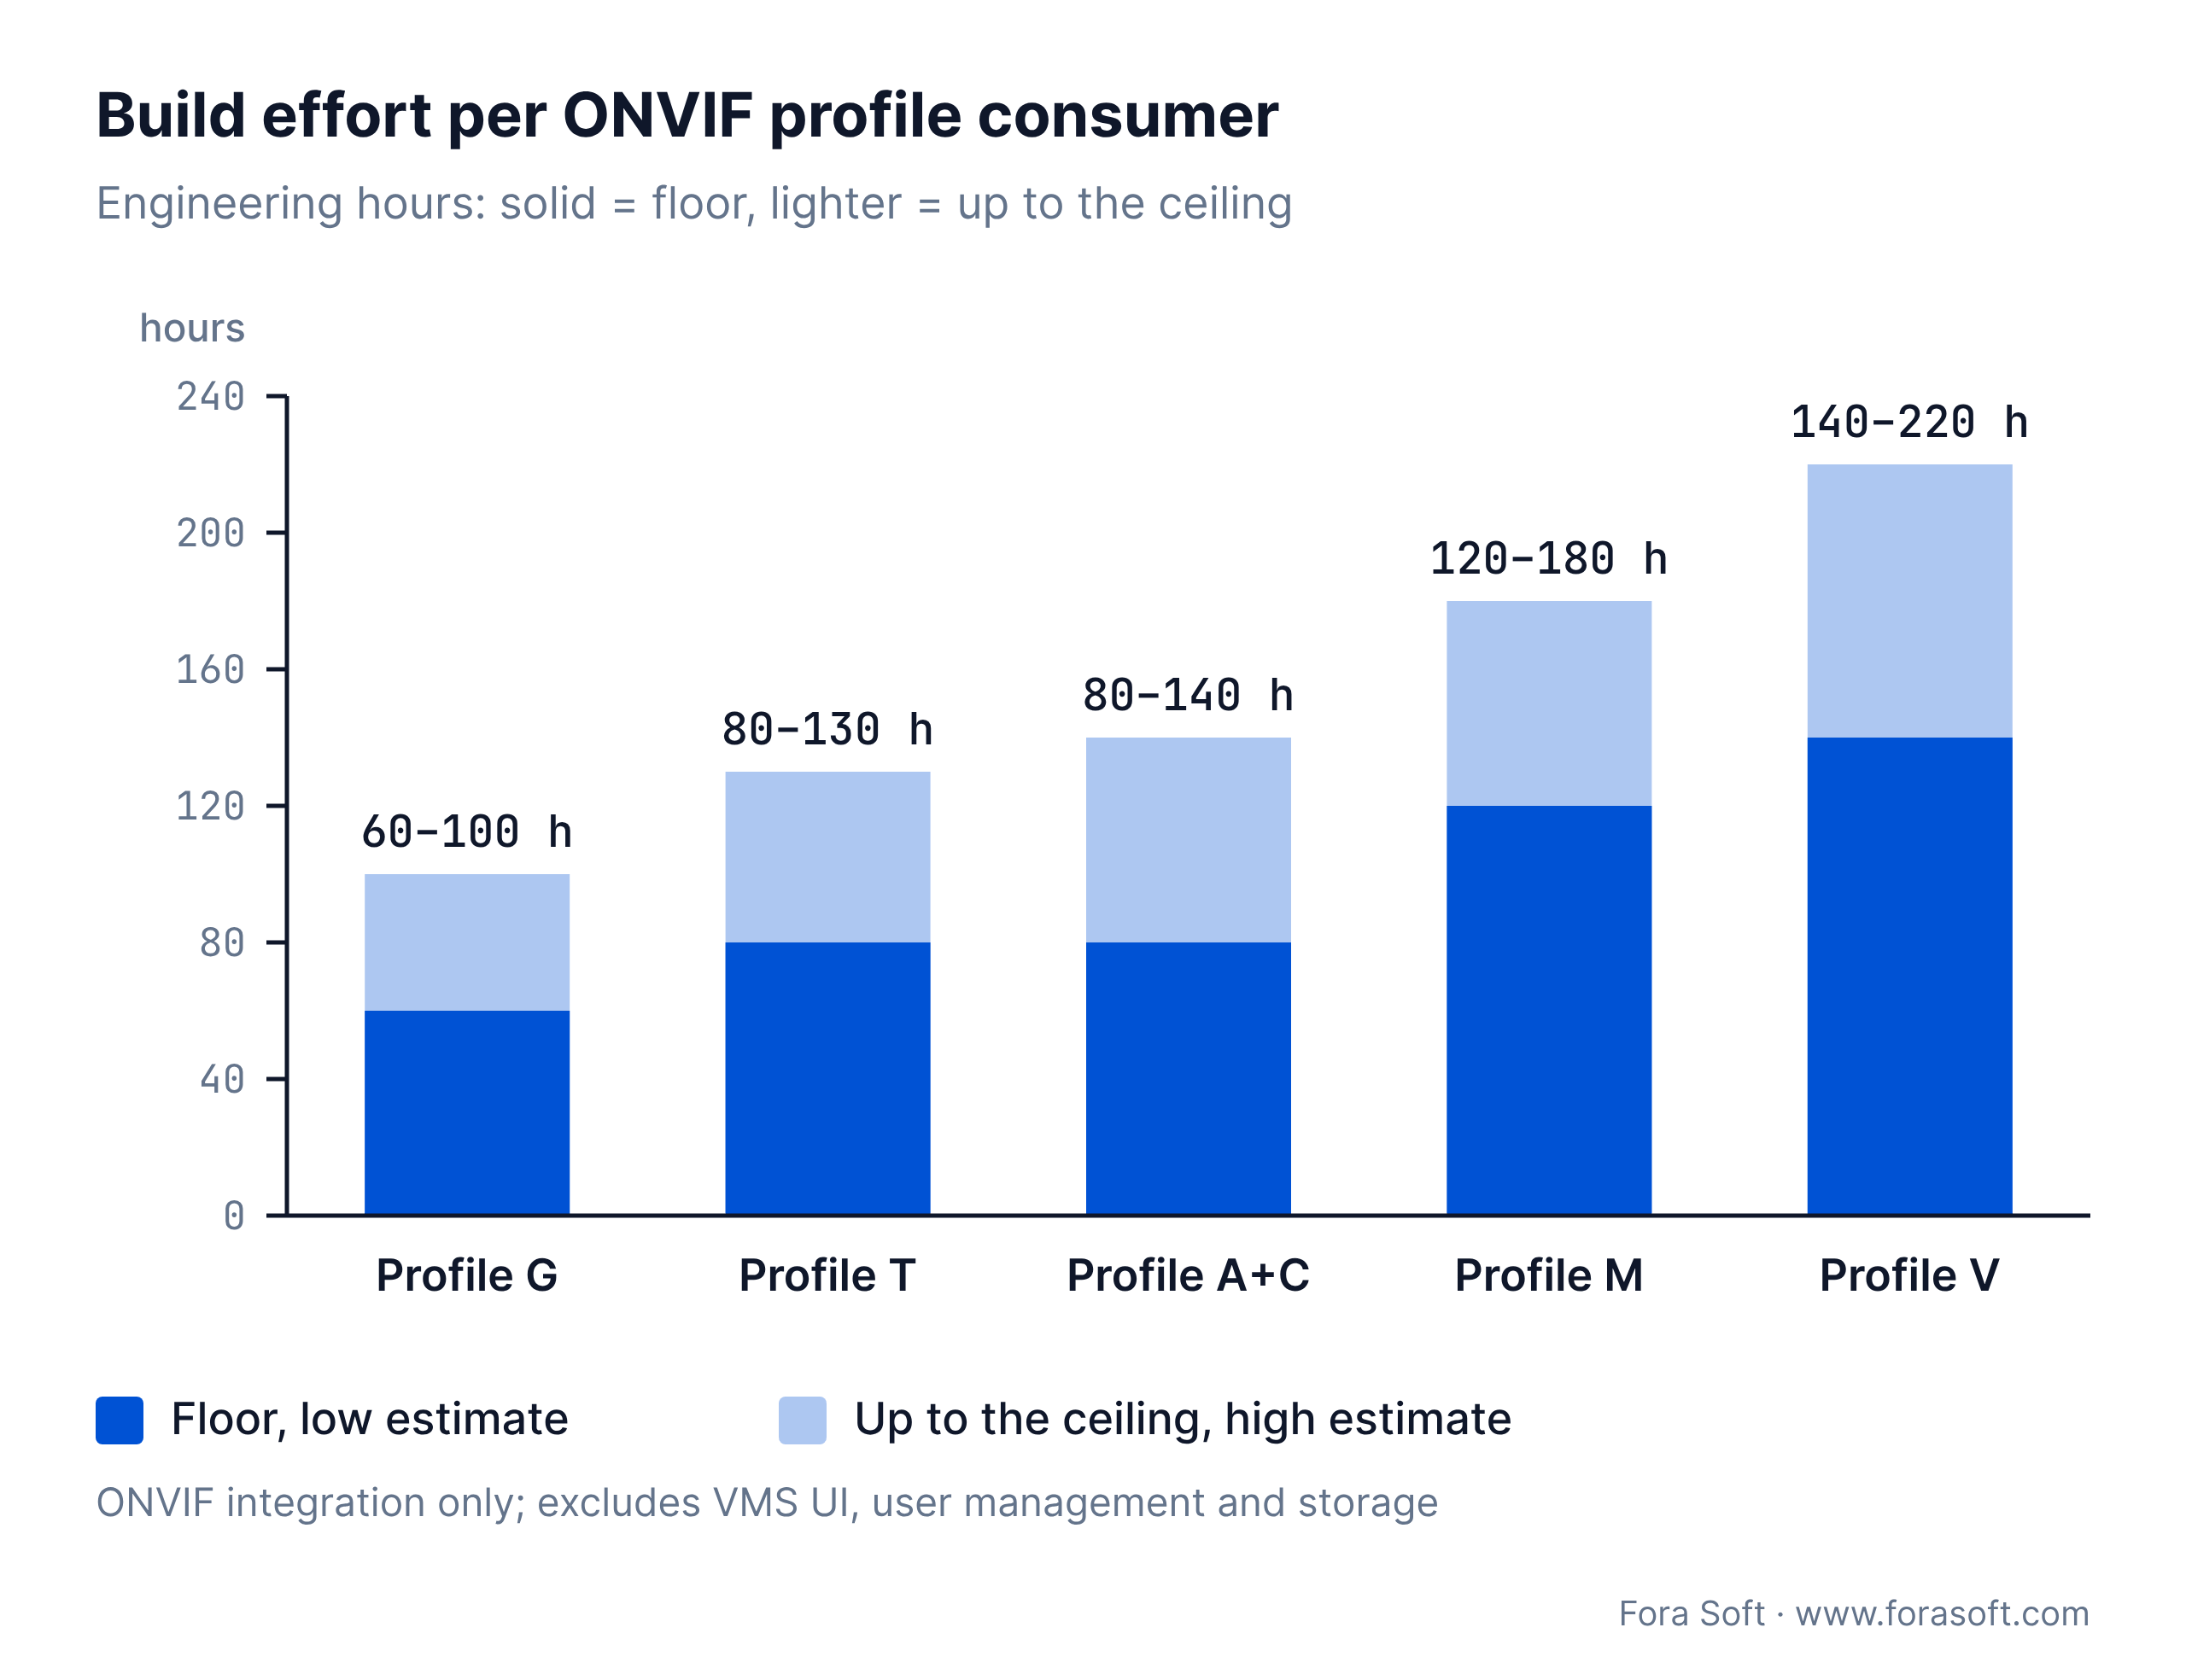
Figure 4. Build effort per ONVIF profile consumer, low-to-high engineering-hour range on our accelerated workflow.
Which profiles to mandate in five questions
Q1. Will you deploy H.265? Yes: Profile T is non-negotiable. No: mandate Profile T anyway, because Profile S stops accepting new conformance on March 31, 2027.
Q2. Will recording live on the edge? Yes: Profile G is required. No, central VMS only: Profile G is optional.
Q3. Is cross-vendor analytics metadata in scope? Yes: Profile M is required, and plan for MQTT plus a metadata archive. No: skip M, proprietary analytics may cost less.
Q4. Is the product cloud-first, or is access control unified with video? Cloud-first: track Profile V and design toward Uplink now. Unified access control: plan Profile A + C, likely D.
Q5. Does procurement include Hikvision or Dahua? Yes: plan a parallel proprietary-SDK path for advanced features and clear the NDAA/FCC filter first. No: pure ONVIF is realistic.
Five pitfalls that sink ONVIF projects
1. Trusting spec sheets over DoCs. Marketing pages overstate conformance. The DoC is the contract, so audit every model.
2. Ignoring firmware pinning. Conformance depends on firmware. A fleet on 12 firmware revisions has 12 different behaviors to support.
3. Assuming optional features work. If a Profile T camera has no tick against “image settings”, you cannot set brightness over ONVIF, even though the web UI can.
4. Conflating ONVIF with the vendor SDK. If the product depends on Axis ACAP, Bosch IVA, Hikvision DeepinView or Wisenet AI, ONVIF alone will not carry the feature.
5. Skipping WS-Discovery governance. On a flat LAN, WS-Discovery multicast floods the network when hundreds of cameras wake at once. Segment the VLAN, or turn off multicast discovery and add devices with a script.
Want an honest ONVIF readiness audit?
Send your camera list and VMS spec. We come back with which profiles to mandate, what to drop, and where the hidden integration costs sit.
KPIs: what to measure on an ONVIF stack
Quality KPIs. Live-stream start latency under 800 ms p95 from PLAY to first I-frame, PTZ command round-trip under 400 ms, and metadata delivery latency under 500 ms where Profile M is used.
Business KPIs. Storage footprint per camera per day (Profile T H.265 should run 40–50% below Profile S H.264), alert-to-operator latency under 1 s, and the number of proprietary SDK code paths: zero on unified sites, one or two at most on mixed fleets.
Reliability KPIs. Camera availability at or above 99.5% per month, ONVIF discovery completion under 30 s for a 500-camera LAN, and no more than three distinct firmware versions across the fleet at any time.
When ONVIF is the wrong tool
Consumer cloud cameras. Ring, Nest and Wyze do not ship ONVIF. For consumer products sold with a cloud backend, proprietary protocols win on latency, battery life and ease of integration.
Sub-100 ms critical-infrastructure alerting. In ultra-low-latency workflows such as perimeter intrusion at nuclear or financial sites, WebRTC with in-band alarm metadata beats the ONVIF event pipeline. Use ONVIF for the archive and the evidentiary chain, and keep the hot path on the faster channel.
Single-vendor, closed ecosystem. If the hardware and VMS come from one vendor and nobody wants to swap either, the native SDK gives more features with less ceremony. ONVIF is insurance for vendor flexibility; if you will never use that flexibility, you can skip the premium.
Reach for a hybrid ONVIF + SDK stack when: your fleet mixes enterprise brands (Axis, Bosch, Hanwha) with budget brands (Hikvision, Dahua) and you need full feature access on both.
FAQ
What are the ONVIF profiles S, T, G, M, A, C and D?
They are fixed feature sets a device or client can conform to. Video profiles: S (basic H.264 streaming, being retired in 2027), T (advanced H.264/H.265 streaming, the 2026 baseline), G (edge recording and playback), M (analytics metadata). Access-control profiles: A (configuration), C (door events), D (peripherals). Profile V, a cloud profile, is a 2026 release candidate. One device can hold several profiles.
Is ONVIF free to use?
Yes, the specifications are free to download. Conformance testing carries a fee paid to ONVIF, and you only need it if you manufacture a device or client and want to show the ONVIF mark. Using ONVIF on existing conformant devices costs nothing in licensing.
Is ONVIF Profile S being discontinued?
Yes. ONVIF announced on October 9, 2025 that it will end support for Profile S. After March 31, 2027, manufacturers cannot submit new products, or existing products with new firmware, for Profile S conformance, because Profile S mandates username-token authentication that falls short of current security guidance. Existing Profile S devices keep working, but new deployments should mandate Profile T.
What is ONVIF Profile V?
Profile V is ONVIF’s cloud video surveillance profile, published as a release candidate on July 9, 2026 (listed as Release Candidate 2.0 in November 2026) and expected to finalize by the end of 2026. The camera opens a secure Uplink to a cloud client over WSS, authenticates with OAuth 2.0 and mutual TLS, streams H.264 over WebRTC and pushes encrypted recordings to cloud storage. A cloud VMS can then mix cameras from multiple vendors without a proprietary cloud in the middle.
Which ONVIF profiles do I need for a cloud VMS?
For a cloud-first or VSaaS product, target Profile V (the 2026 cloud release candidate) so cameras from multiple vendors reach your cloud over a device-initiated Uplink. Keep Profile T as the on-premises streaming fallback, add Profile G if you also record at the edge, and Profile M if you need analytics metadata. Until devices ship with Profile V conformance, most cloud builds still run Profile T plus a gateway.
Does Profile T include Profile S?
Not formally. The two overlap heavily, and a Profile T device almost always keeps Profile S features for backward compatibility, but conformance is separate. In practice a Profile T camera from 2021 or later works with Profile S clients. Confirm it in the DoC instead of assuming it from the spec.
Do Hikvision or Dahua cameras support ONVIF?
Yes. Both are ONVIF members, and most of their IP camera lineup ships Profile S and T. Their flagship analytics and advanced storage sit behind proprietary ISAPI and DH-SDK interfaces, so those features need the vendor SDK even on an ONVIF-compliant device. US buyers must also check NDAA and FCC status, which tightened through 2025 and 2026.
Does ONVIF work over the public internet?
The classic profiles were built for the LAN, so terminate ONVIF inside a VPN or a bastion gateway and never expose a camera directly to the public internet. Profile V changes this for cloud: it defines a device-initiated Uplink secured with TLS and OAuth 2.0, the right way to reach a camera through a firewall.
What is the difference between ONVIF Profile S and Profile T?
Profile S is the original H.264 streaming profile; Profile T adds H.265, image settings, tampering events and bidirectional audio, and replaces username-token authentication with digest or TLS. ONVIF stops accepting new Profile S conformance on March 31, 2027 and names Profile T as the successor, so specify Profile T for any new camera or VMS.
How do ONVIF and OSDP help reduce vendor lock-in in security systems?
ONVIF standardizes the IP interfaces between cameras, access controllers and the VMS (Profiles S, T, G, M for video; A, C, D for access control). OSDP, the SIA protocol approved as international standard IEC 60839-11-5 in 2020, standardizes the secure link between card readers and door controllers. With both in place you can swap the camera, reader, controller or software brand without rewriting integrations.
What is the ONVIF Media Signing Add-on?
It is an ONVIF release candidate, announced on August 26, 2026, in which cameras and encoders sign video cryptographically at encoding time. A verification tool can then prove the footage was not altered and trace it to the source device. The final specification is expected at the end of 2026; version 1 covers video only.
What is ONVIF Profile G?
ONVIF Profile G is the edge recording and playback profile, finalized in 2014. It lets a VMS configure recording on a camera or NVR, search the stored footage and play it back without a vendor SDK; its mandatory features are digest authentication, recording search and replay control.
What is the latest ONVIF version?
ONVIF releases its network interface specifications twice a year; the latest is release 26.06 from June 2026, which added SRTP to the streaming specifications. Profiles have their own versions, and the newest profile, Profile V, is still a release candidate in November 2026.
Is ONVIF the same as RTSP?
No. RTSP is a media streaming protocol. ONVIF is a management and control standard that uses RTSP, among other protocols, to move media. You can talk RTSP to a camera without ONVIF, but you will not get PTZ, analytics events or unified discovery.
What to Read Next
Profile M deep dive
ONVIF Profile M and Object Detection
How Profile M wires analytics metadata across multi-vendor surveillance fleets.
VMS design
12 Essential Features of Modern VMS Software
Where ONVIF support fits inside the modern VMS feature matrix.
Architecture
Scalable Video Management Systems
Five engineering decisions that shape a scalable VMS, ONVIF among them.
Buying guide
Best IP Camera Systems for Business
NDAA-aware sourcing and the specs that matter before the ONVIF audit.
Ready to make ONVIF a competitive advantage?
ONVIF holds modern IP surveillance together, and the sticker on the box only opens the conversation. Read the DoC, mandate Profile T now that Profile S is on a 2027 clock, add G and M where the deployment needs them, watch Profile V for cloud, and plan around the places where vendor SDKs still carry the advanced features. Clear the NDAA and FCC filter before any of it. Done well, an ONVIF-native system costs less to run, is easier to refresh and is protected against vendor strategy changes nobody can predict today.
Fora Soft has built ONVIF consumers, VMS back-ends and gateways for over a decade, including the platform behind 770+ US organizations on VALT. If you want to skip the learning curve, we bring the reference architecture, the code and the operational playbook from retail, smart-city, industrial, courtroom and enterprise-security projects. More build notes are in our custom VMS development guide.

The handbook · 7 volumes
Fora Soft Video Engineering Handbook
Once you know which profiles to mandate, the camera fleet still has to push streams your VMS can record, play back and analyse at scale. We wrote a seven-volume handbook on that stack; start with the volume on transport, ingest, RTSP-style contribution and latency budgets, then the encoding volume for H.264 and HEVC settings, and the AI volume for detection and tracking on the feeds. Written by Nikolay Sapunov, CEO at Fora Soft.
Browse the handbook on Amazon →7 volumes · 9,000+ pages · Kindle & paperback
Let’s turn ONVIF into an unfair advantage
Bring your camera list, your VMS requirements, and any proprietary SDK pain you are living with. We will map the shortest, cleanest path forward.

